Data Protection and Hosting: GDPR and Provider Checks
A hosting provider can support your data-protection work, but cannot make an entire website compliant simply by putting its server in a particular country. The website’s data collection, application settings, contracts and connected services matter too.
This educational checklist was reviewed against official guidance on 18 October 2026. It is not a legal assessment of your organisation. Use it to prepare questions for a qualified adviser and the suppliers handling your data.
First establish which rules apply
GDPR scope is not determined solely by citizenship or the server’s address. Article 3 covers processing in the context of an EU establishment and certain activities of organisations outside the EU, including offering goods or services to people in the Union or monitoring relevant behaviour there. Read the regulation and assess the actual processing.
Other national and sector-specific rules can apply alongside data protection. Do not assume that a guide about GDPR resolves health, payment or other regulated-data requirements. Record the applicable regime and any effective dates before choosing a service.
Map the data, including services outside the main host
Start with a practical inventory: contact forms, account records, orders, mailboxes, analytics, logs and backups. Note why each is needed, where it goes, who can access it and how long it is kept.
A hosting region might cover the database without covering a remote backup, support tool or third-party analytics service. Ask suppliers for the locations and access arrangements relevant to the specific product. Keep answers with a date and the service name.
Clarify the controller and processor relationship
The website operator will often determine the purposes of processing, while a hosting supplier may process data on its behalf. Roles depend on the activity, so the same supplier can have different roles for different processing.
The EDPB’s controller and processor guide explains the required contract and responsibilities. For the proposed arrangement, review instructions, security, sub-processors, assistance with rights requests and what happens to data when the service ends.
A standard data-processing agreement can be a useful starting point. Its availability is not proof that your configuration or every connected service satisfies your requirements. Make unresolved points part of the supplier review.
Assess international transfers separately from storage
GDPR restricts qualifying transfers outside the EEA; it does not impose a universal rule that every covered database must remain there. The EDPB transfer guidance describes adequacy decisions, appropriate safeguards and limited derogations.
Ask which organisations receive or can access the relevant data, from where, and under which mechanism. An EEA storage choice does not answer every question about another organisation’s remote access or onward processing.
The European Commission’s current adequacy information includes participating US commercial organisations under the EU-US Data Privacy Framework. Do not apply that status to every US supplier. Verify the recipient, scope and current position for the transfer you intend to make.
Ask how security matches the risk
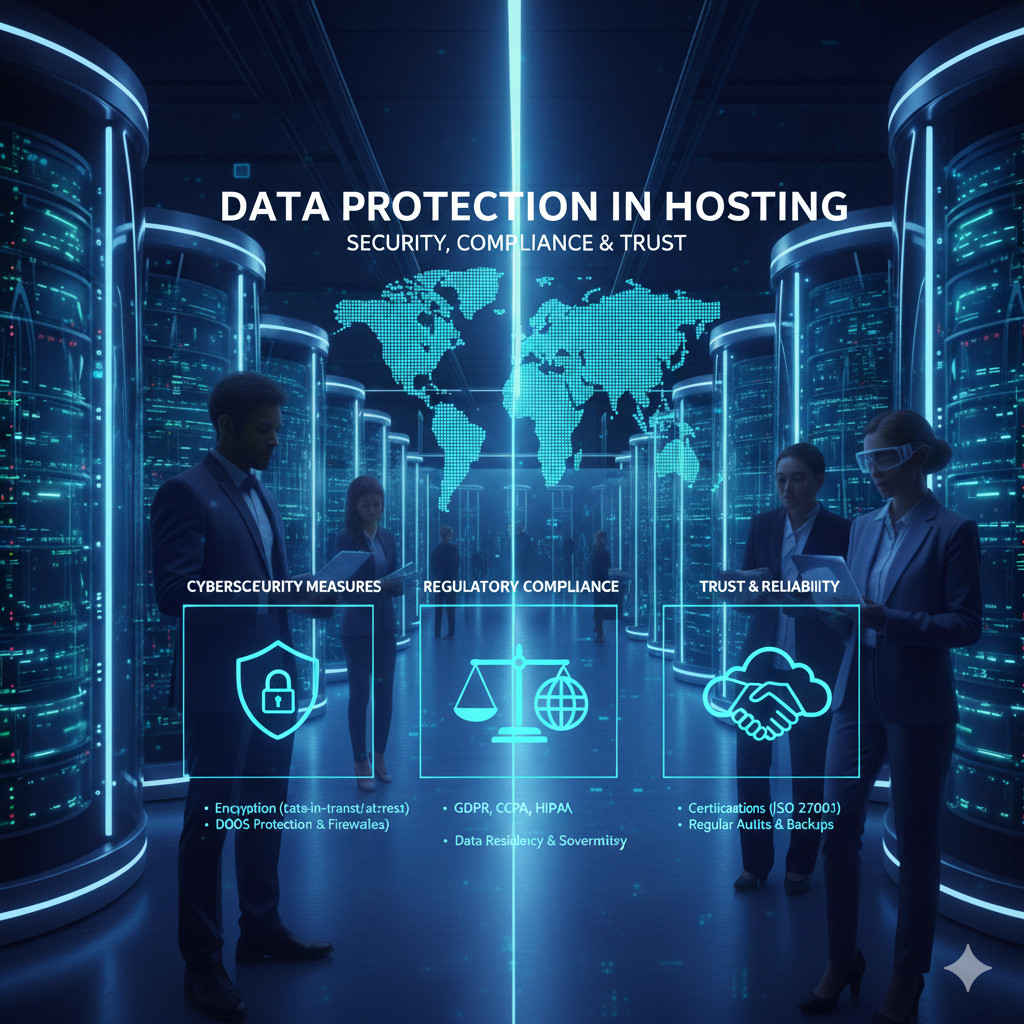
GDPR Article 32 takes a risk-based approach to appropriate technical and organisational measures. It does not reduce compliance to buying a certificate or installing a fixed list of products.
Discuss access controls, encryption and key handling, patching, recovery, testing and incident response. The EDPB security guide provides a starting point. Obtain the scope and date of audit evidence rather than treating an ISO or SOC badge as a guarantee for the whole website.
Include incidents, deletion and the way out
Ask who contacts you about an incident, how quickly information becomes available and how it supports your own notification decisions. Reporting duties depend on the role, circumstances and applicable rules; a universal deadline detached from those conditions is misleading.
Check how a rights request reaches hosted data and how deletion or return works at termination. Ask about retained logs, backup expiry and restoration that could reintroduce previously removed information. Document the operating procedure as well as the supplier’s answer.
For an India-related service, check commencement too
India notified the DPDP Rules in 2025 with phased implementation. The government’s official announcement describes that approach. Confirm the operative provisions, notifications and any sector-specific requirements for your situation rather than assuming every provision began on the same day.
Turn the review into a buying decision
Record required features, the supporting contract and evidence, the person responsible and any open question. Resolve material gaps before migration. The local and global hosting guide covers geography, while the migration checklist helps plan a controlled transfer once the service is suitable.